Information Security Management Consulting
Helping organisations improve their security posture through practical governance and risk management.
Services
Practical information security consulting to help organisations manage risk, meet regulatory requirements and implement effective security capabilities.
Security Governance, Strategy & Risk
Establish clear security priorities, governance and risk-based decision-making aligned with business needs.
Effective information security is built upon clear priorities, responsibilities and governance. My engagements typically start with assessing the security posture, identifying strengths, weaknesses, gaps and risks; I help organisations define strategies, governance structures and target operating models that align security activities with business objectives.
The scope can include a full risk assessment, focus on getting policies and controls into shape, or involve mapping out what capabilities you actually need and how to build them. The goal is to turn security requirements into practical structures and processes that can be implemented, operated and sustained.
Compliance, Audit & Regulatory Readiness
Prepare for security audits and regulatory assessments, address control gaps and remediate findings effectively.
Audits and regulatory assessments require more than just documentation. For a successful audit, organisations need to figure out which rules actually apply, where their controls are solid and where gaps need to be remediated. I help organisations prepare the processes, evidence and stakeholders needed for a successful assessment.
The work shifts depending on where you are. Sometimes it’s a readiness check, sometimes it’s fixing gaps under pressure, sometimes it’s preparing the management team for the actual conversations, or addressing findings afterward. I’ve done this across SOC 2, ISO 27001 and BSI IT-Grundschutz, as well as regulatory requirements and examinations involving BaFin and section 44 KWG.
Security Transformation & Implementation
Turn security requirements into effective processes, technologies and operational capabilities.
Security improvements often require coordinated changes across technology, processes and organisational structures. I help translate security requirements and strategic objectives into implementable solutions — from scoping, requirements and solution design through to implementation, integration and operational transition.
Engagements can include security monitoring and SIEM/SOC build-outs, incident management, application and cloud security, IAM, vulnerability management and other security-control enhancements. I coordinate across internal teams, technology providers and external service partners to help move initiatives from concept to live operation.
AI Security & Secure Adoption
Manage the security risks of AI while enabling its responsible adoption in business and technology environments.
AI creates new opportunities, but also new risks for applications, data, access, and established security processes. I help organisations integrate security into AI adoption and the development of AI-enabled products.
That includes assessing AI-specific security risks, defining governance and controls, addressing data and access requirements, and integrating AI security into existing software development, application, cloud, and information security processes. The aim is to make AI adoption effective without treating security as an afterthought.
Expertise
Security Governance & Risk
Security strategy, governance frameworks, risk and gap assessments, target operating models, policies and controls.
Application, Cloud & AI Security
Secure software development, application and cloud security, IAM, vulnerability management and secure AI adoption.
Security Operations & Incident Management
SOC and SIEM transformation, security monitoring, detection engineering, incident management and response.
Compliance, Audit & Security Standards
Audit preparation and execution, remediation of regulatory findings and security frameworks including SOC 2, ISO 27001, NIST CSF and BSI IT-Grundschutz.
Selected Projects
TECHNOLOGY & CONSULTING
Security Transformation for a Cloud Application
I led a full security transformation for a cloud-based application, from SOC 2 readiness and gap assessment through to the implementation of security processes and technical controls. The engagement covered secure software development, application and cloud security, IAM, vulnerability management and responsible AI adoption.
Financial Services
Security Monitoring & Regulatory Remediation
I designed and implemented security monitoring capabilities to address regulatory and audit requirements. The work covered governance and policies, SIEM implementation, application and infrastructure monitoring, risk-based detection use cases, response playbooks and coordination with internal teams and external service providers.
Manufacturing
Incident Management for Manufacturing Environments
I designed an IT security incident management process for manufacturing sites and integrated it with the central SOC. The engagement included the definition of responsibilities, escalation paths and response structures across central organisations and site-level teams, followed by pilot implementation, change management and training at production locations.
About me
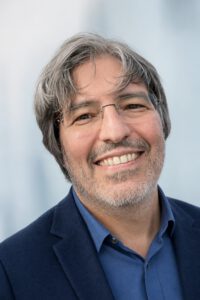
Alessandro Guida
I am an information security consultant with more than 20 years of international experience across financial services, technology, telecommunications, manufacturing and government.
My work covers security governance and strategy, risk and compliance, security operations, application and cloud security, and security transformation. I work at the intersection of management and technology, combining technical and architectural experience with programme leadership to turn security requirements into controls, processes and operating models that actually work.
I have worked independently since 2011, with clients ranging from international banks and industrial companies to technology providers and public-sector organisations. I combine strategic advice with hands-on implementation, working directly with management, security teams, engineers, and external providers to deliver sustainable improvements.
Certifications
CISSP
Certified Information Systems Security Professional
CCSP
Certified Cloud Security Professional
ISO 27001 CIS LA
Certified ISMS Lead Auditor
PMP
Project Management Professional
Contact
If you are looking for support with an information security initiative, assessment or transformation, feel free to get in touch. Tell me briefly what you are working on, and I will get back to you.
Prefer email? alessandro [at] guida-ism.net